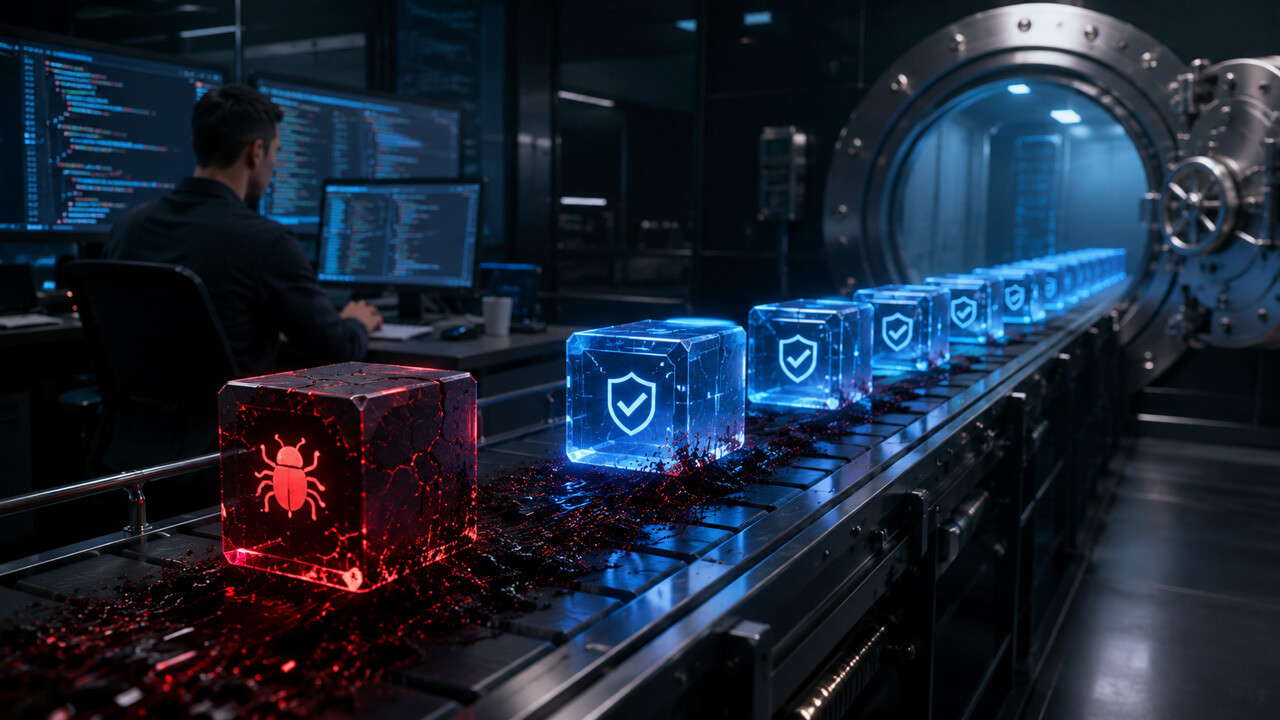
Every major DeFi post-mortem concludes with the same finding: the vulnerability was in the code. Auditors missed it. Developers wrote it. Attackers found it. The implicit assumption is that the attack begins when the exploit transaction is broadcast. Security researchers are increasingly convinced that this model is wrong — the next generation of DeFi exploits begins months before deployment, in the development environment.
The DeFi development stack is built on open-source dependencies: Hardhat, Foundry, OpenZeppelin contracts, Ethers.js, Alchemy SDK. A compromised dependency injected into any of these tools can modify contract compilation output without changing the source code a developer reads. The compiled bytecode deployed to mainnet contains the backdoor; the source code in the repository does not.
This attack vector moved from theoretical to demonstrated in 2024 when a malicious package was published to npm that intercepted private key generation in Ethereum wallet libraries used by several DeFi teams. The packages had legitimate names with subtle typos — a classic typosquatting attack applied to crypto-specific libraries. The attack was caught before significant funds were drained, but only because a security researcher was monitoring npm for suspicious packages targeting crypto keywords.
Most DeFi protocols use continuous integration pipelines to automate testing and deployment. These pipelines run in cloud environments with access to deployment keys, contract upgrade admin keys, and sometimes multisig signing infrastructure. A compromised CI/CD environment can intercept the deployment process and substitute a malicious contract for the audited version.
"You can audit the code perfectly and still deploy a compromised contract. The audit covers what's in the repository. It does not cover what runs in the build pipeline."
Reproducible builds — where the bytecode deployed to mainnet can be independently reconstructed from source code by any external party — provide partial protection against pipeline compromise. Ethereum's Sourcify project enables on-chain source verification. Several protocols now require multisig deployment with participants who independently verify bytecode checksums before signing.
Dependency pinning — locking all npm and Foundry dependencies to specific hashes rather than version ranges — prevents dependency hijacking after an initial audit. This practice is standard in enterprise software security but inconsistently applied in DeFi development.
The uncomfortable conclusion is that the security boundary for DeFi protocols extends far beyond the smart contract code. It encompasses every tool used to write, test, compile, and deploy that code. Until the industry treats the entire supply chain as the attack surface — not just the deployed contract — pre-deployment exploits will remain an underestimated and underprepared-for risk category.
Keywords: Culture|DeFi|Featured|Scams
Source: CryptoSlate.com